The result-oriented AI SOC

Results, not alerts.

You don’t need another place to look at alerts. You need them closed, reported and proven.

Ingext is the AI SOC that does the work and hands you the result.

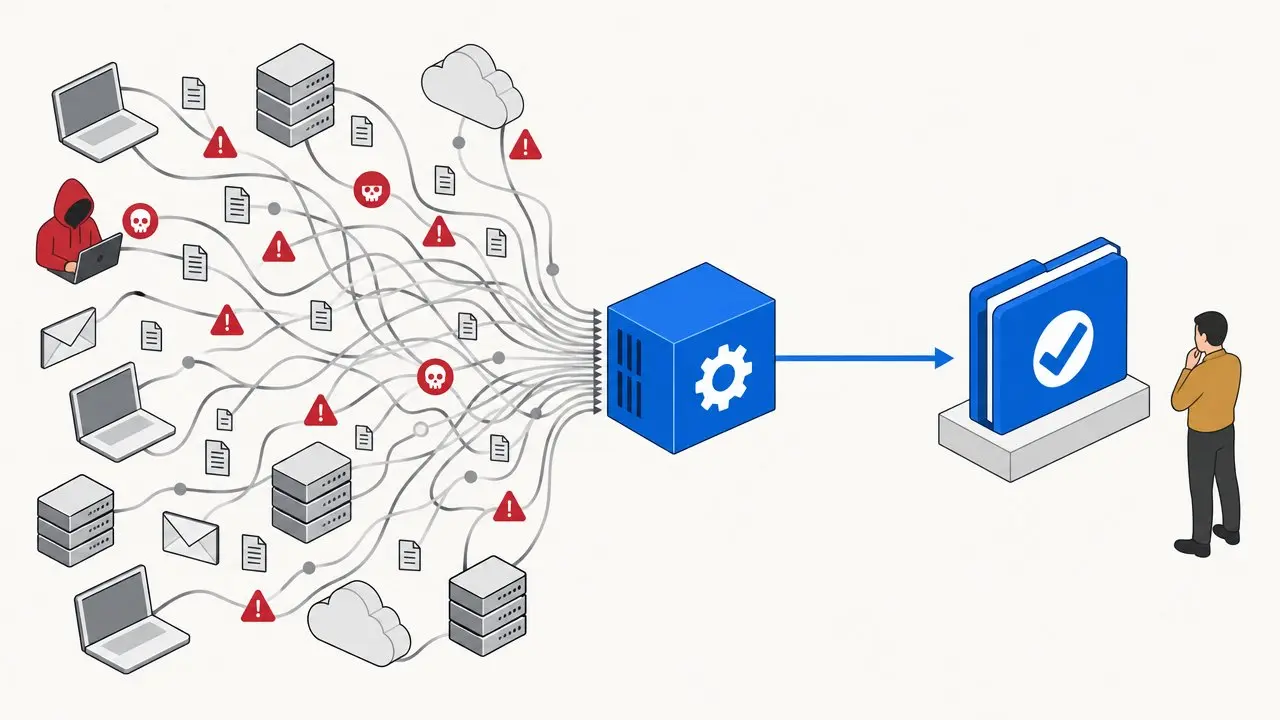
Hundreds of tangled event streams and alerts go in; one closed, checked case comes out

What a result looks like

Three things land on your desk. None of them is an alert.

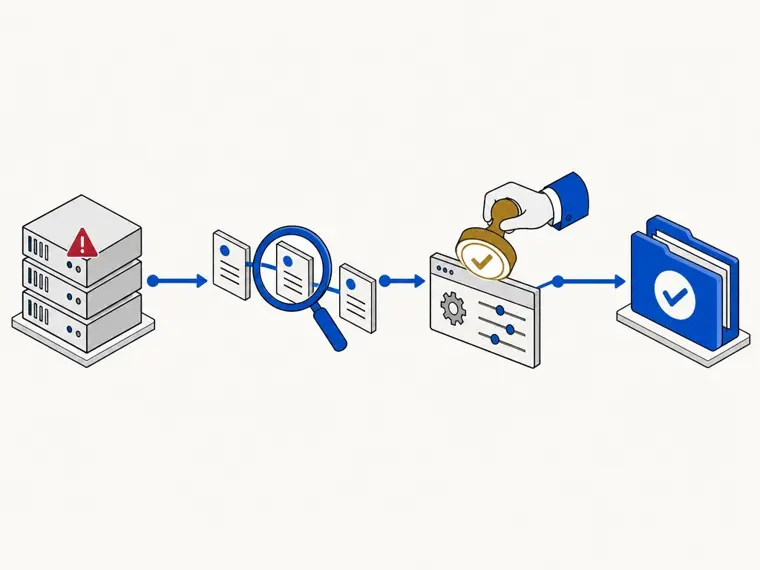
A flagged server, the records that prove what happened, an approval stamp on the fix, and a closed case folder
R1

An issue, closed.

For example: a service account starts signing in from a country it has never used. You don’t get an alert to chase. You get the case closed: what happened, the records that prove it, the fix it carried out, and the check that shows it held.

See our threat coverage →
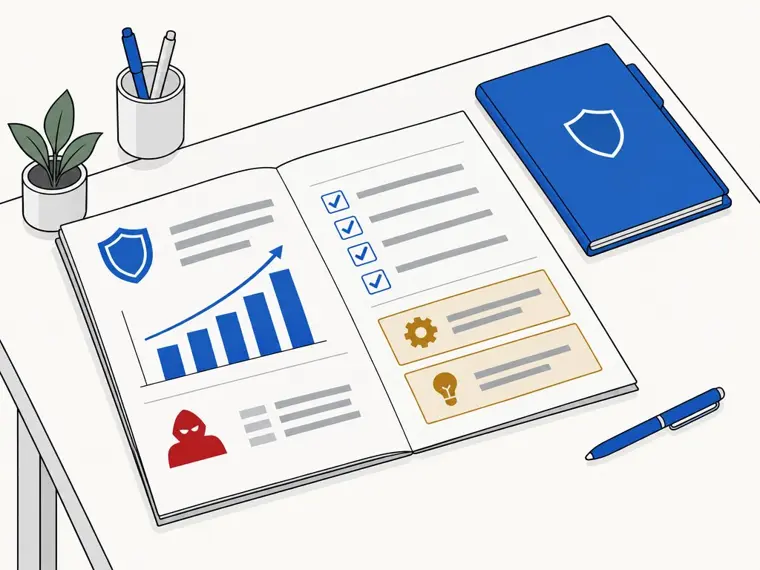
An open monthly security briefing with an upward trend, completed items and two highlighted decisions
R2

A report leadership can act on.

Every month: where security stands, what improved, what’s still open, and the one or two decisions that need you. Written from the evidence, not assembled by hand the night before.

See the reporting →
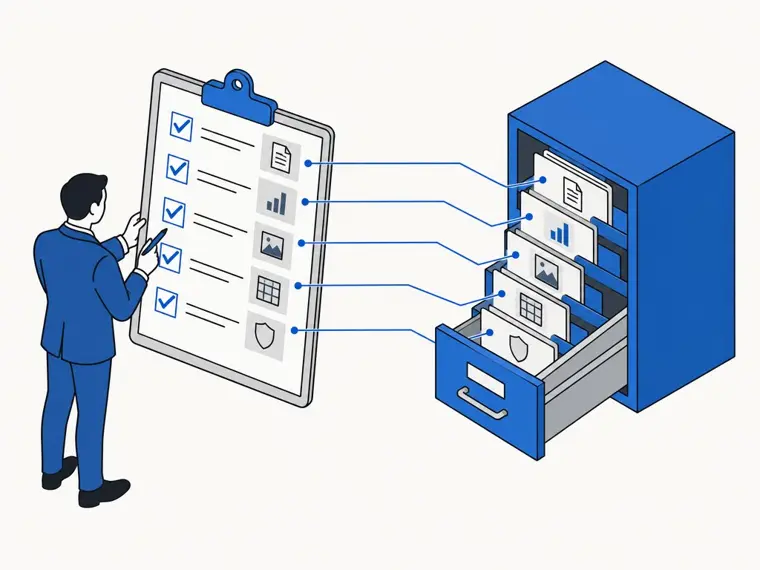
An auditor’s checklist where every control is already linked to dated evidence in a filing drawer
R3

Proof, ready for the audit.

When an auditor asks how you know MFA is enforced, the answer is already collected, dated and tied to the control.

See the compliance reports →

A teammate, not another console

It talks to your team in Microsoft Teams or Slack.

No new screen to watch. Ingext works in the channel your team already uses, like a colleague: what it found, what it did about it, and what it needs from you. A small browser companion is there when you want the detail.

  • It tells you what it did. When it closes something, the channel hears what happened, what it fixed and where the proof is.
  • It asks when your rules say to. Routine fixes run on their own. Anything you’ve marked as needing a person waits for a reply.
  • It answers questions. Ask in plain English and it answers from the evidence, across your whole history.
# securityTeams · Slack
  1. Ingext

    Closed: svc-backup was signing in from a country it has never used. It was a stolen credential. I revoked 2 live sessions and reset the password.

    Case evidence and timeline

  2. Ingext

    One more step needs an OK first: blocking that sign-in location for everyone would also block a travel vendor. Go ahead?

    ApproveNot now

  3. Dana

    Approve. Did anyone else sign in from there?

  4. Ingext

    No. I checked 12 months of sign-ins across every account. Nothing else. Blocked, and it’s in Friday’s report.

Example conversation · fictional names

It gets better every time

Every closed issue makes the next one faster.

When Ingext closes an issue, it keeps what it learned: the pattern, the proof and the fix that worked. Then it checks the rest of your history for the same pattern, so the next one is caught sooner, or never opens at all.

  1. Spot: finds the issue in your data, including the ones no alert would raise.
  2. Prove: gathers the records that show exactly what happened.
  3. Decide: you confirm what it is: real, or an admin doing their job.
  4. Fix: carries out the fix itself, within the approval rules you set.
  5. Confirm: checks that the fix held, then closes the case with the proof attached.
  6. Learn: searches your history for the same pattern, so the next one is caught sooner.

You make the call. The AI does the rest, including the fix.

How a SOC matures with AI →
the result loopevery close makesthe next one faster1spot2prove3decide4fix5confirm6learn
The AI does itYou decide

Why Ingext can promise a result

AI can’t close what it can’t see.

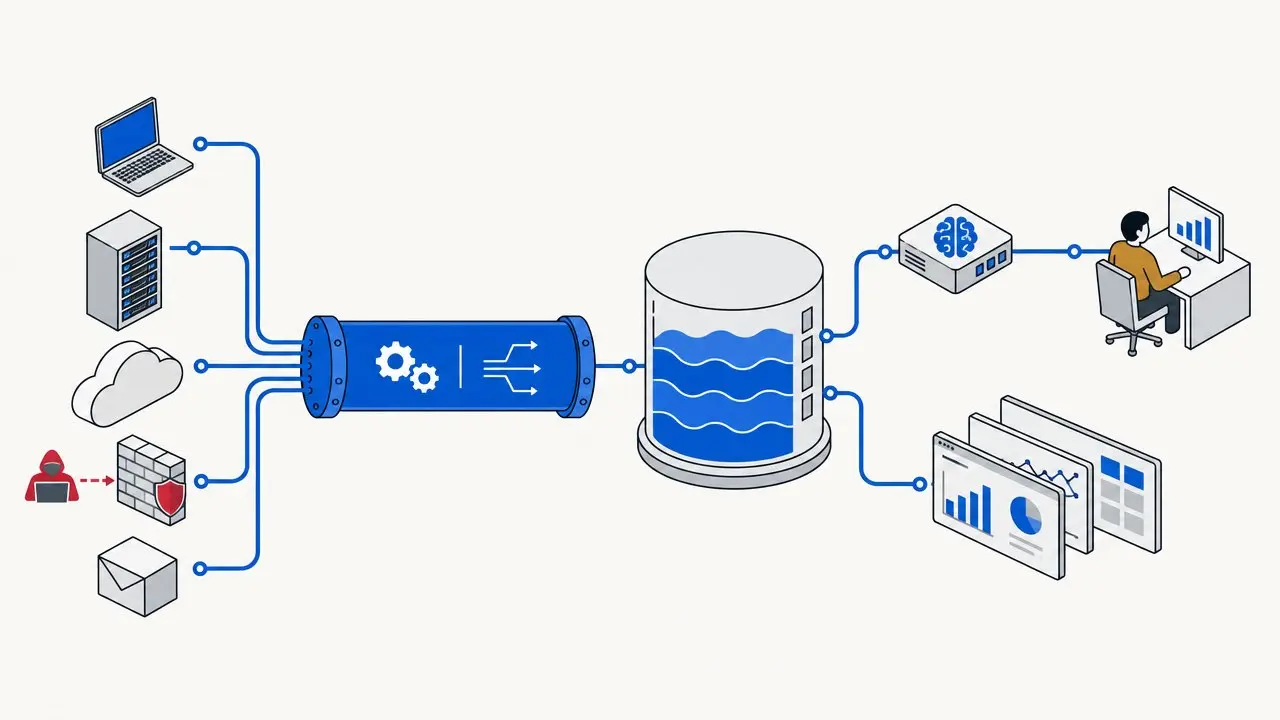
Most AI SOC tools borrow their data from other tools, and lose the trail when that data expires. Ingext started as the data pipeline. It collects your security data once, cleans it, adds context and keeps the history in storage you own.

So every investigation has the whole picture, and so does every report.

Security sources flow through one pipeline into a data lake you own, which feeds both the AI and your own analytics

A SIEM gives your team a place to work. Ingext gives you the result.

With a SIEM

Your team searches, triages, chases and writes it up.

With Ingext

You review the result and make the call.

See what’s new in Ingext →

Insights & research

Latest from our blog

How attacks really unfold, how AI is changing the SOC, and what it takes to turn security data into decisions.

What Is AiTM, and Why It Matters
Article

What Is AiTM, and Why It Matters

Adversary-in-the-middle (AiTM) phishing steals Microsoft 365 sessions after MFA succeeds and gives attackers free rein over the mailbox. Here is what a real AiTM attack looked like, and how Fluency no...

FS

Ingext

Research

Read More
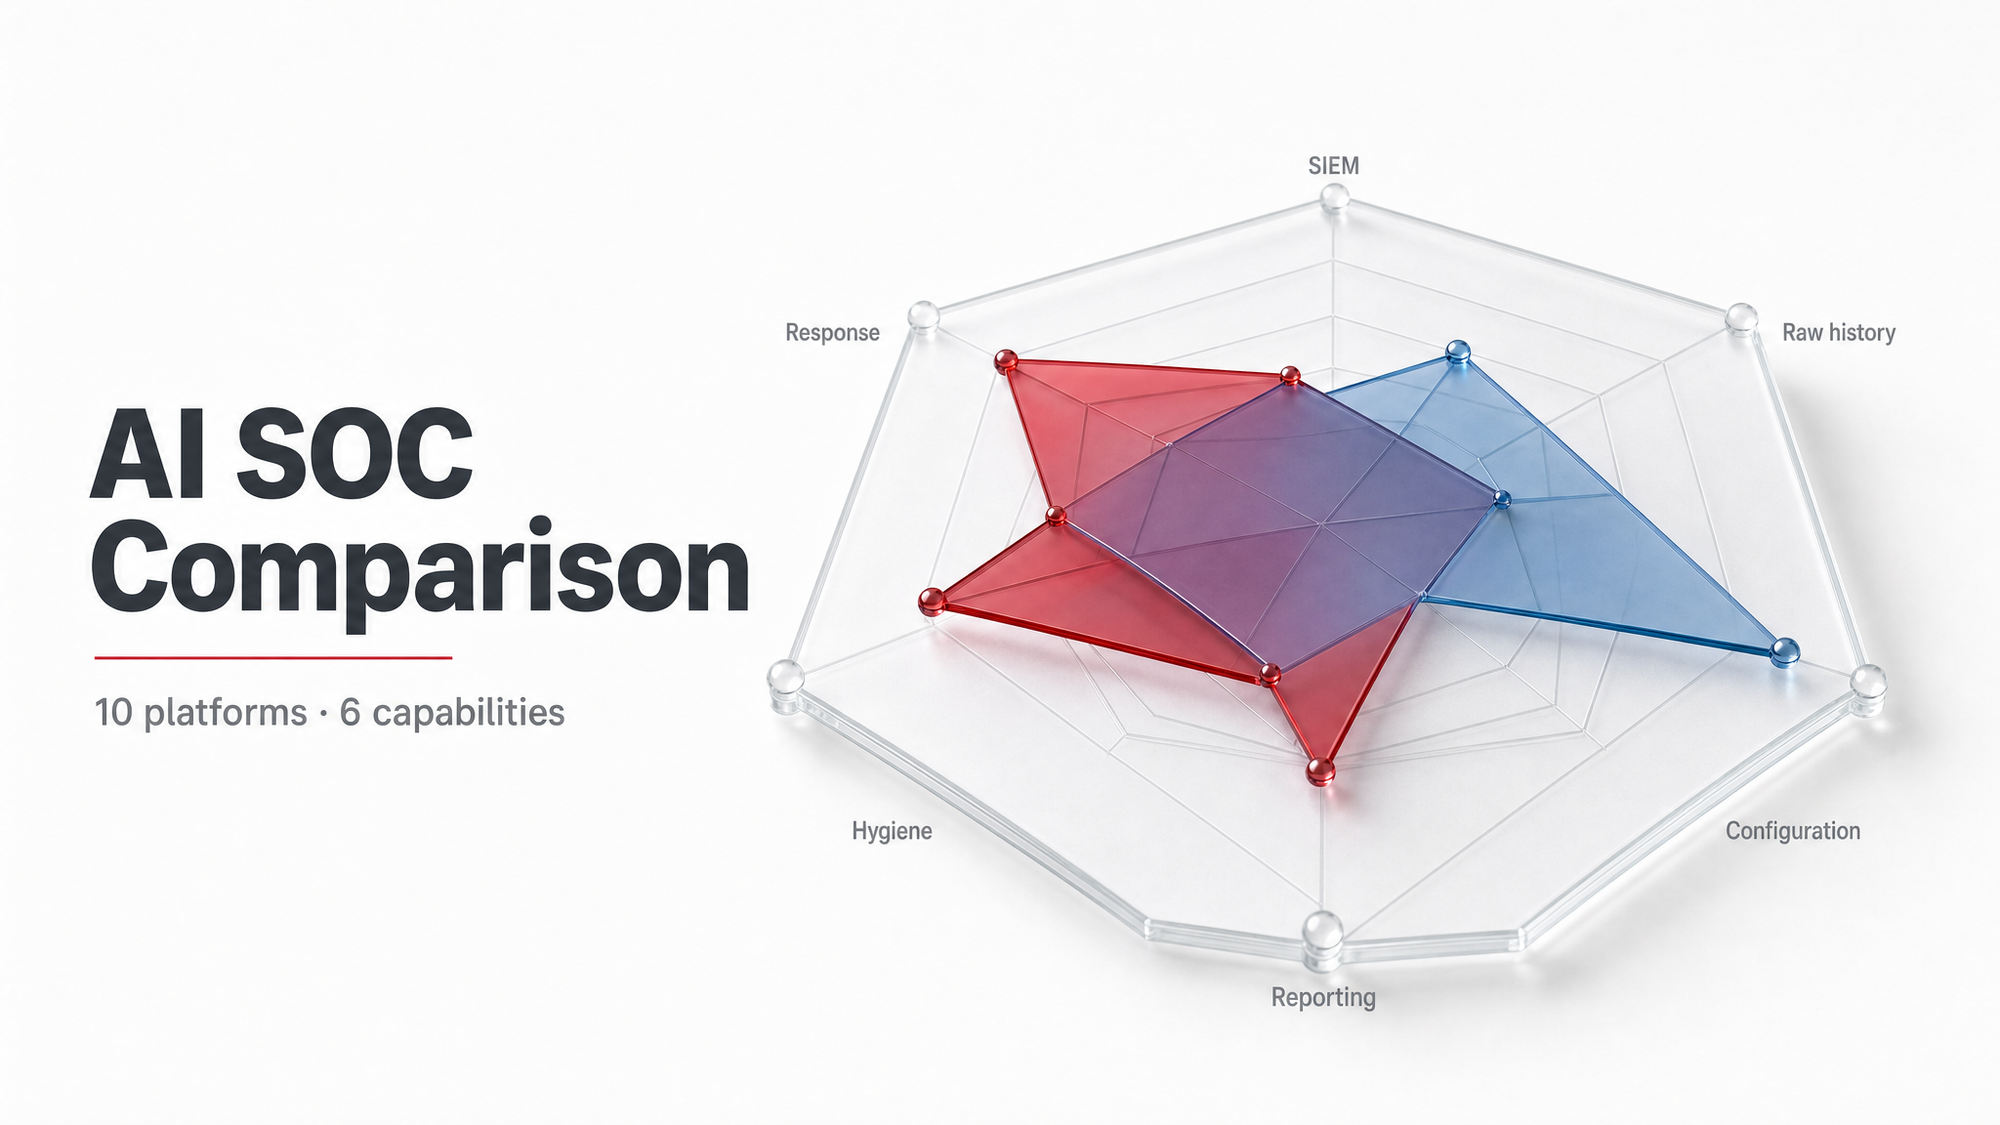
Beyond the AI SOC label
AI

Beyond the AI SOC label

We compared ten AI SOC platforms. AI investigation is the shared promise. The real differences are in the data a platform keeps, the environment it understands, the reports it delivers and the actions...

FS

Ingext

Research

Read More

Next step

Bring us one open issue.

Tell us about one issue that has been sitting open. We’ll walk it to closure with you, on your own data.

Talk to Sales
sales@ingext.io
Need Support?
support@ingext.io